On day 3 of a developer community’s “30-Day Open-Source Contribution Challenge,” with a 50,000 USDC prize pool, a technical failure outrages its real contributors.
The challenge is meant to encourage developers to make at least 1 valid Commit to a designated open-source repository every day, record completion on-chain, and split the deposits of unsuccessful participants after 30 days. But the development team takes a shortcut: users click “check in,” the frontend checks their GitHub status locally, then opens MetaMask to call the contract’s checkIn() function.
Scripted reward farmers quickly find the fatal gap: the contract never verifies the off-chain GitHub contribution. Anyone can bypass the frontend and submit contract transactions directly to simulate successful check-ins with 100% reliability. In just 2 hours, automated scripts give more than 800 empty wallets perfect-attendance records, threatening to dilute and redistribute the deposits of developers who actually wrote code.
Smart contracts run in isolated virtual-machine sandboxes. They cannot initiate HTTP requests to the GitHub REST API, read Twitter/X repost data, or cheaply iterate over every DEX’s cross-chain trade history. A useful Web3 task-growth and check-in platform needs an architectural connection between Off-Chain Task Evaluation and On-Chain Cryptographic Attestation.
Using production practices from ChainPunch, this article explains how EIP-712 Attestation Tickets enable secure, cheat-resistant hybrid-task check-ins at high concurrency.
1. Security Challenges in Off-Chain Task Verification
Mapping real off-chain actions into a blockchain state machine introduces four major threats:
+----------------------------------------------------------------------------------------------------+
|                               Four Hybrid-Task Verification Attack Surfaces                        |
+----------------------------------------------------------------------------------------------------+

   [ Attack 1: Ticket Replay ]
   An attacker captures a valid Day 1 signature and resubmits it on Day 2 or Day 3 to claim repeatedly.

   --------------------------------------------------------------------------------------------------

   [ Attack 2: Subject Mismatch / Front-Running ]
   Alice completes a high-quality code contribution. Bob sees her attestation in the public Mempool,
   substitutes his wallet address, and broadcasts first to steal credit for her work.

   --------------------------------------------------------------------------------------------------

   [ Attack 3: Stale Attestation Window ]
   A user obtains proof 3 days earlier, then reverts the GitHub contribution or cancels a third-party DEX trade,
   but still tries to use the expired ticket on-chain after the deadline to claim rewards.

   --------------------------------------------------------------------------------------------------

   [ Attack 4: Cross-Domain Signature Forgery ]
   An attacker submits a Ticket issued for a testnet or another challenge to the current mainnet challenge contract.
+----------------------------------------------------------------------------------------------------+
2. Designing One-Time EIP-712 Attestation Tickets
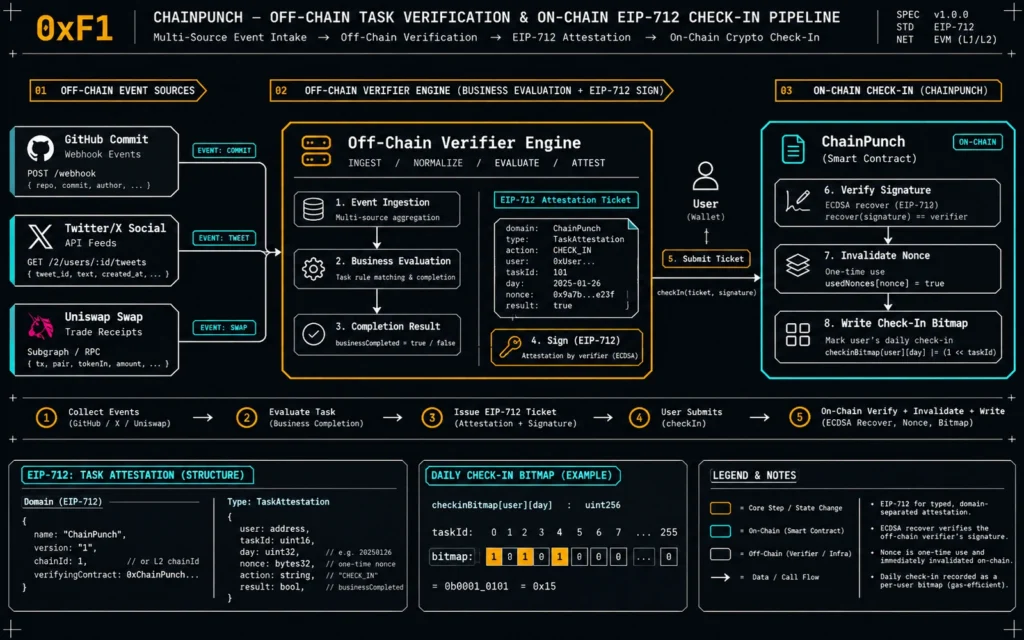
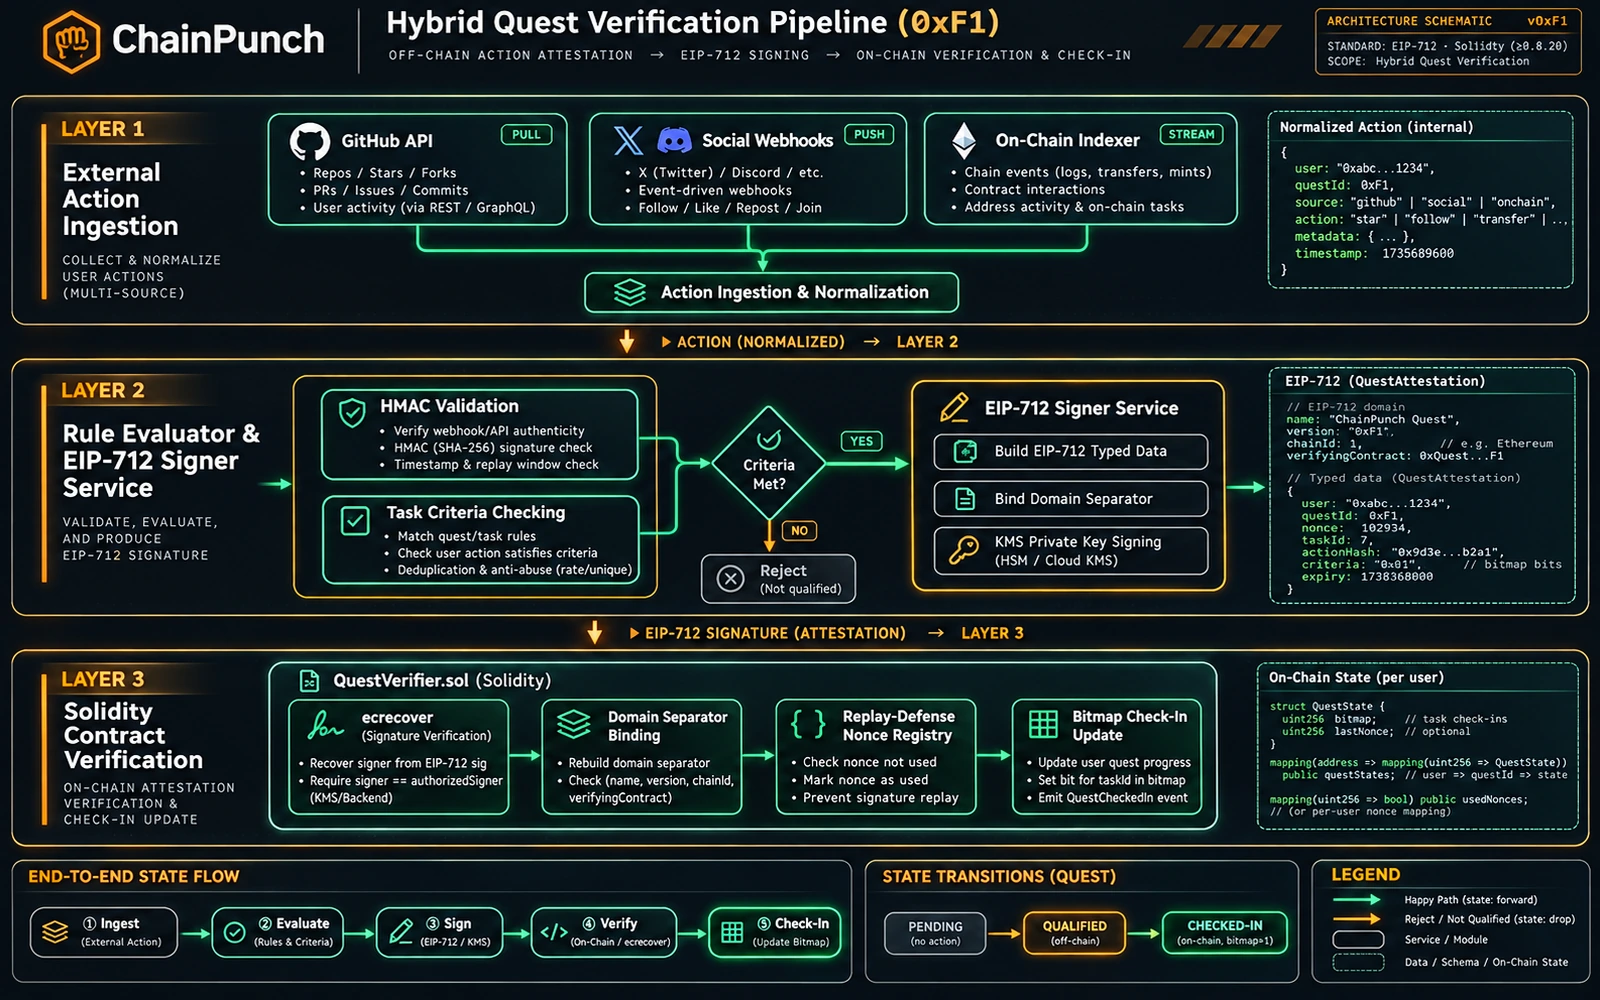
The production ChainPunch design uses three layers: off-chain monitoring and evaluation → tightly constrained EIP-712 ticket issuance → on-chain redemption with user-paid gas:
+----------------------------------------------------------------------------------------------------+
|                               ChainPunch Hybrid-Task Check-In Topology                             |
+----------------------------------------------------------------------------------------------------+

   [ Off-Chain Task Sources ]
   ├── GitHub Webhooks (Commit / merged PR events)
   ├── Social APIs (reposts / Discord binding)
   └── On-chain indexers (e.g. actual Uniswap volume >= 100 USDC)
                 │
                 ▼ Unified ingestion
   [ ChainPunch Rule Evaluation Engine ]
   1. Verify the wallet bound to the GitHub user exactly matches msg.sender (prevent subject substitution)
   2. Verify a genuine qualifying action occurred within today's calendar day
   3. Sign an EIP-712 Attestation Ticket using secure KMS / an authorized node private key
                 │
                 ▼ Return to frontend
   [ User Wallet ]
   Holds the Ticket and calls `checkInWithAttestation(ticket, signature)`
                 │
                 ▼
   [ On-Chain Contract (ChainPunchChallenge.sol) ]
   1. Verify the authorized evaluator's signature (ecrecover)
   2. Check block.timestamp <= ticket.expiresAt (prevent expired replay)
   3. Check ticket.user == msg.sender (prevent interception and front-running)
   4. Mark ticket.nonce consumed in the replay-protection bitmap (one use)
   5. Atomically write userCheckInBitmap (check-in complete)
+----------------------------------------------------------------------------------------------------+
3. Solidity Signature Verification and Replay Protection
The contract must use the EIP-712 Domain Separator to bind chainId and the current contract address, preventing cross-contract and cross-chain replay:
// checkin-task/contracts/src/ChainPunchTaskVerifier.sol
// SPDX-License-Identifier: MIT
pragma solidity ^0.8.20;

import "@openzeppelin/contracts/access/Ownable2Step.sol";
import "@openzeppelin/contracts/utils/cryptography/ECDSA.sol";
import "@openzeppelin/contracts/utils/cryptography/EIP712.sol";
import "@openzeppelin/contracts/utils/ReentrancyGuard.sol";

error SignatureExpired();
error InvalidAttestationSigner();
error NonceAlreadyConsumed(uint256 nonce);
error SubjectMismatch(address expected, address actual);
error TargetDayAlreadyCheckedIn(uint256 dayIndex);

contract ChainPunchTaskVerifier is EIP712, Ownable2Step, ReentrancyGuard {
    using ECDSA for bytes32;

    bytes32 private constant ATTESTATION_TICKET_TYPEHASH = keccak256(
        "AttestationTicket(address user,uint256 challengeId,uint256 dayIndex,bytes32 taskCriteriaHash,uint256 nonce,uint64 expiresAt)"
    );

    address public trustedTaskSigner; // Public key of the official off-chain rule verification service

    // nonce => whether consumed (ticket replay protection)
    mapping(uint256 => bool) public consumedNonces;
    // userAddress => 256-bit check-in bitmap
    mapping(address => uint256) public userCheckInBitmap;

    event TaskCheckInCompleted(
        address indexed user,
        uint256 indexed challengeId,
        uint256 indexed dayIndex,
        bytes32 taskCriteriaHash,
        uint256 nonce
    );

    struct AttestationTicket {
        address user;
        uint256 challengeId;
        uint256 dayIndex;
        bytes32 taskCriteriaHash; // Task metadata hash (e.g. Commit SHA + Repo ID)
        uint256 nonce;            // Unique one-time nonce
        uint64 expiresAt;         // Absolute expiry timestamp
    }

    constructor(
        address _trustedSigner,
        address initialOwner
    ) EIP712("ChainPunchTaskGateway", "1") Ownable(initialOwner) {
        trustedTaskSigner = _trustedSigner;
    }

    function setTrustedSigner(address _newSigner) external onlyOwner {
        require(_newSigner != address(0), "INVALID_SIGNER");
        trustedTaskSigner = _newSigner;
    }

    /**
     * @notice Core on-chain check-in entry using an EIP-712 ticket
     */
    function checkInWithAttestation(
        AttestationTicket calldata ticket,
        bytes calldata signature
    ) external nonReentrant {
        // 1. Prevent front-running: caller must match the ticket beneficiary
        if (msg.sender != ticket.user) {
            revert SubjectMismatch(ticket.user, msg.sender);
        }

        // 2. Enforce expiry: current block time must not exceed the ticket expiry
        if (block.timestamp > ticket.expiresAt) {
            revert SignatureExpired();
        }

        // 3. Prevent replay: Nonce must never have been used
        if (consumedNonces[ticket.nonce]) {
            revert NonceAlreadyConsumed(ticket.nonce);
        }

        // 4. Prevent duplicate check-ins: the day must not already be recorded
        uint256 bitmap = userCheckInBitmap[msg.sender];
        if ((bitmap & (1 << ticket.dayIndex)) != 0) {
            revert TargetDayAlreadyCheckedIn(ticket.dayIndex);
        }

        // 5. Verify the EIP-712 signature came from the authorized official node
        bytes32 structHash = keccak256(abi.encode(
            ATTESTATION_TICKET_TYPEHASH,
            ticket.user,
            ticket.challengeId,
            ticket.dayIndex,
            ticket.taskCriteriaHash,
            ticket.nonce,
            ticket.expiresAt
        ));

        bytes32 digest = _hashTypedDataV4(structHash);
        address recoveredSigner = digest.recover(signature);

        if (recoveredSigner != trustedTaskSigner) {
            revert InvalidAttestationSigner();
        }

        // 6. Atomically consume the Nonce and set the bitmap bit
        consumedNonces[ticket.nonce] = true;
        userCheckInBitmap[msg.sender] = bitmap | (1 << ticket.dayIndex);

        emit TaskCheckInCompleted(
            msg.sender,
            ticket.challengeId,
            ticket.dayIndex,
            ticket.taskCriteriaHash,
            ticket.nonce
        );
    }
}
4. Off-Chain Node.js / TypeScript Evaluation and Signing Service
ChainPunch runs a lightweight evaluation daemon on the server. When a user requests task verification, the service calls the third-party API in real time and signs structured data only after confirming completion:
// checkin-task/src/services/attestation-signer.service.ts
import { Injectable, UnauthorizedException, BadRequestException } from '@nestjs/common';
import { privateKeyToAccount } from 'viem/accounts';
import { keccak256, toHex } from 'viem';

export interface GenerateTicketParams {
  userWallet: `0x${string}`;
  challengeId: bigint;
  dayIndex: bigint;
  githubUsername: string;
  repo: string;
}

@Injectable()
export class AttestationSignerService {
  private signerAccount = privateKeyToAccount(process.env.TASK_SIGNER_PRIVATE_KEY as `0x${string}`);
  private chainId = 8453; // Base Mainnet
  private contractAddress = process.env.TASK_VERIFIER_CONTRACT_ADDRESS as `0x${string}`;

  /**
   * @notice Issue a one-time EIP-712 check-in ticket after verifying the GitHub Commit
   */
  public async verifyAndSignGithubTask(params: GenerateTicketParams) {
    // 1. Business validation: call the GitHub API to check for a valid commit today
    const hasValidCommit = await this.checkGithubCommitToday(params.githubUsername, params.repo);
    if (!hasValidCommit) {
      throw new BadRequestException('No valid GitHub commits detected for today in specified repository.');
    }

    // 2. Construct a replay-protection Nonce and a 5-minute validity window
    const now = Math.floor(Date.now() / 1000);
    const expiresAt = BigInt(now + 300); // Valid for 300 seconds
    const nonce = BigInt(Date.now()) * 1000n + BigInt(Math.floor(Math.random() * 1000));

    // 3. Hash task details (Repo + date + Commit fingerprint) with Keccak256 for the audit trail
    const taskCriteriaHash = keccak256(toHex(`github:${params.repo}:${params.githubUsername}:${params.dayIndex}`));

    const domain = {
      name: 'ChainPunchTaskGateway',
      version: '1',
      chainId: BigInt(this.chainId),
      verifyingContract: this.contractAddress,
    };

    const types = {
      AttestationTicket: [
        { name: 'user', type: 'address' },
        { name: 'challengeId', type: 'uint256' },
        { name: 'dayIndex', type: 'uint256' },
        { name: 'taskCriteriaHash', type: 'bytes32' },
        { name: 'nonce', type: 'uint256' },
        { name: 'expiresAt', type: 'uint64' },
      ],
    };

    const message = {
      user: params.userWallet,
      challengeId: params.challengeId,
      dayIndex: params.dayIndex,
      taskCriteriaHash: taskCriteriaHash,
      nonce: nonce,
      expiresAt: expiresAt,
    };

    // 4. Sign according to EIP-712
    const signature = await this.signerAccount.signTypedData({
      domain,
      types,
      primaryType: 'AttestationTicket',
      message,
    });

    return {
      ticket: {
        user: params.userWallet,
        challengeId: params.challengeId.toString(),
        dayIndex: params.dayIndex.toString(),
        taskCriteriaHash,
        nonce: nonce.toString(),
        expiresAt: expiresAt.toString(),
      },
      signature,
    };
  }

  private async checkGithubCommitToday(username: string, repo: string): Promise<boolean> {
    // In production: use Octokit to query commits and compare authors and timestamps
    return true;
  }
}
5. Comparison: Frontend Checks, Oracles, and EIP-712 Tickets
The three hybrid-task verification approaches differ substantially in implementation cost, security, and user experience:
| Dimension | A: Frontend Check + Direct Contract Call | B: Traditional Oracle (Chainlink Functions) | C: ChainPunch EIP-712 Tickets |
|---|---|---|---|
| Scripted-cheating protection | None (anyone can bypass the frontend) | High (decentralized nodes execute HTTP requests by consensus) | Very high (a one-time Ticket signed by the official KMS is required) |
| Gas per task | Low (~25,000 gas) | Very high (oracle callbacks often require expensive LINK fees) | Very low (basic ecrecover and bit operations, ~35,000 gas) |
| Response time | Immediate | Very slow (oracle polling and block inclusion usually take 1~3 minutes) | Millisecond-level (server issuance within seconds, on demand) |
| Flexibility and privacy | Poor | Complex (API Tokens require multiparty custody and can hit limits) | Excellent (server can integrate GitHub, Twitter, or private APIs) |
| Replay and front-running protection | No replay protection | RequestId-based replay protection | Nonce bitmap + strict msg.sender binding |
6. Integration with Grace Periods and Reward Distribution
Hybrid verification gives the challenge platform a real business use and tightly connects to the underlying system:
- Time handling and grace periods: When combined with on-chain daily check-in time engineering and grace periods, the Ticket’s
dayIndexmust align exactly with on-chain calendar-day Epochs and the 15-minute cross-day grace window, allowing valid completions to redeem despite timezone differences or congestion. - Efficient bitmap reward settlement: Verified state writes directly to the single-slot
userCheckInBitmap. At settlement, the no-iteration O(1) distribution algorithm from the on-chain community check-in and challenge DApp architecture supports complex, multi-period challenges for thousands of participants at low cost.
Architecture Consulting and Source-Code Delivery
If you are planning a community-driven Web3 developer task platform, collaborative coding challenge, Trading Quest, or decentralized incentive application and want a hybrid architecture combining credible cheat resistance with a strong user experience:
- Visit Fone client deliveries and system demos to explore the full ChainPunch production workflow for task verification, EIP-712 ticket issuance, and on-chain check-ins;
- Read our 12-Point Engineering and Security Audit for Production Web3 Launches;
- Book a one-to-one technical discussion through the Fone architecture consulting channel for a delivery package with Foundry contract source, NestJS signing middleware, and replay-protection tests.