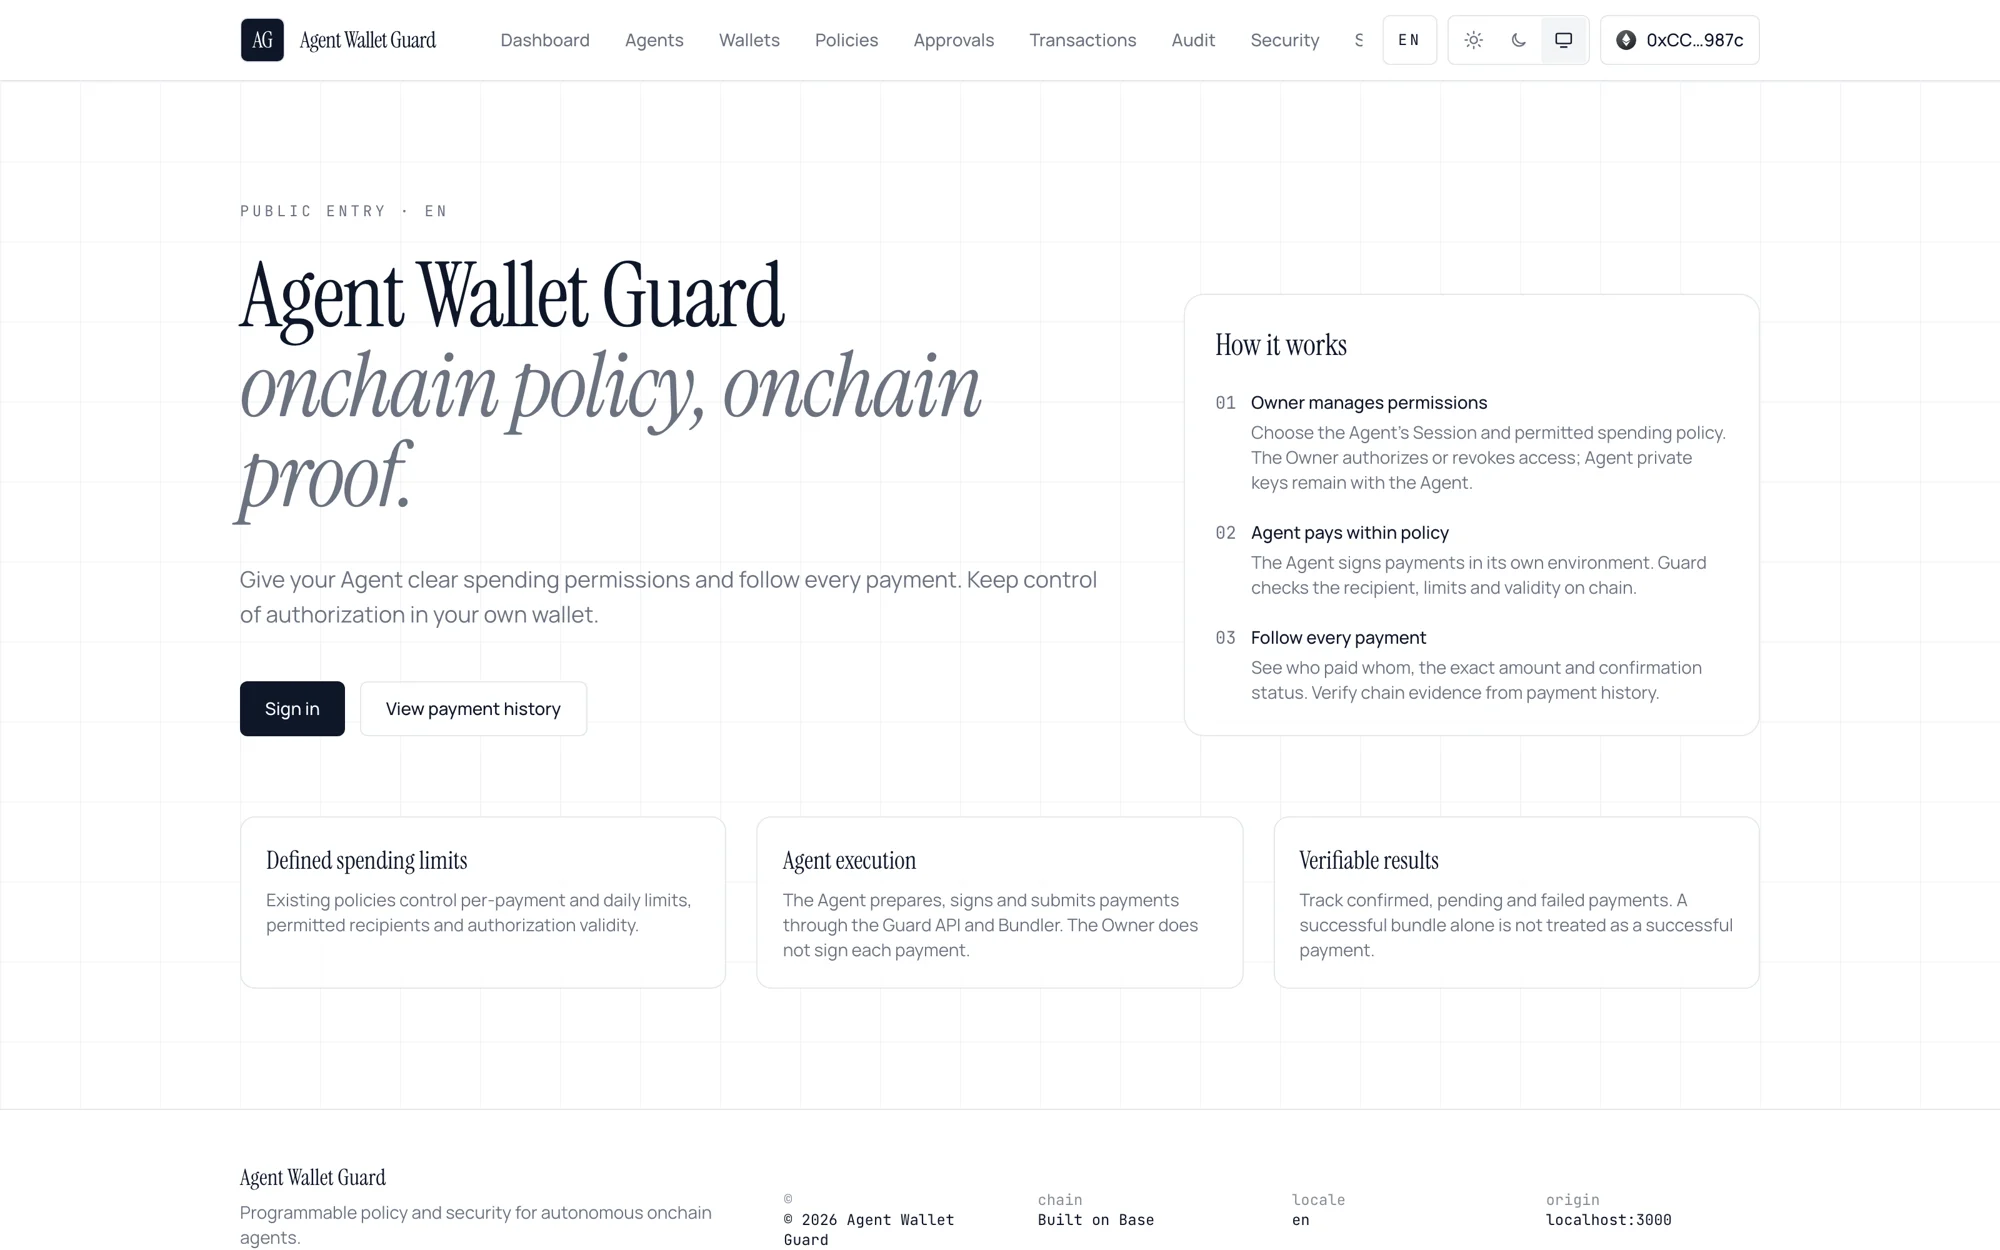
Identify the provider, payment asset, budget and stop conditions, then assess account and chain compatibility. The implemented permission and execution components provide the starting point; LLM decisions and real providers still require integration.
Agent payment entryDemo excerpt · Full screenshot
02 / Integration & customization
Fit permission management to your business
Build on policy review, grants, payments and revocation. Policy creation, organization identity, cost centers, paid plans and real wallet compatibility are separately scoped work.
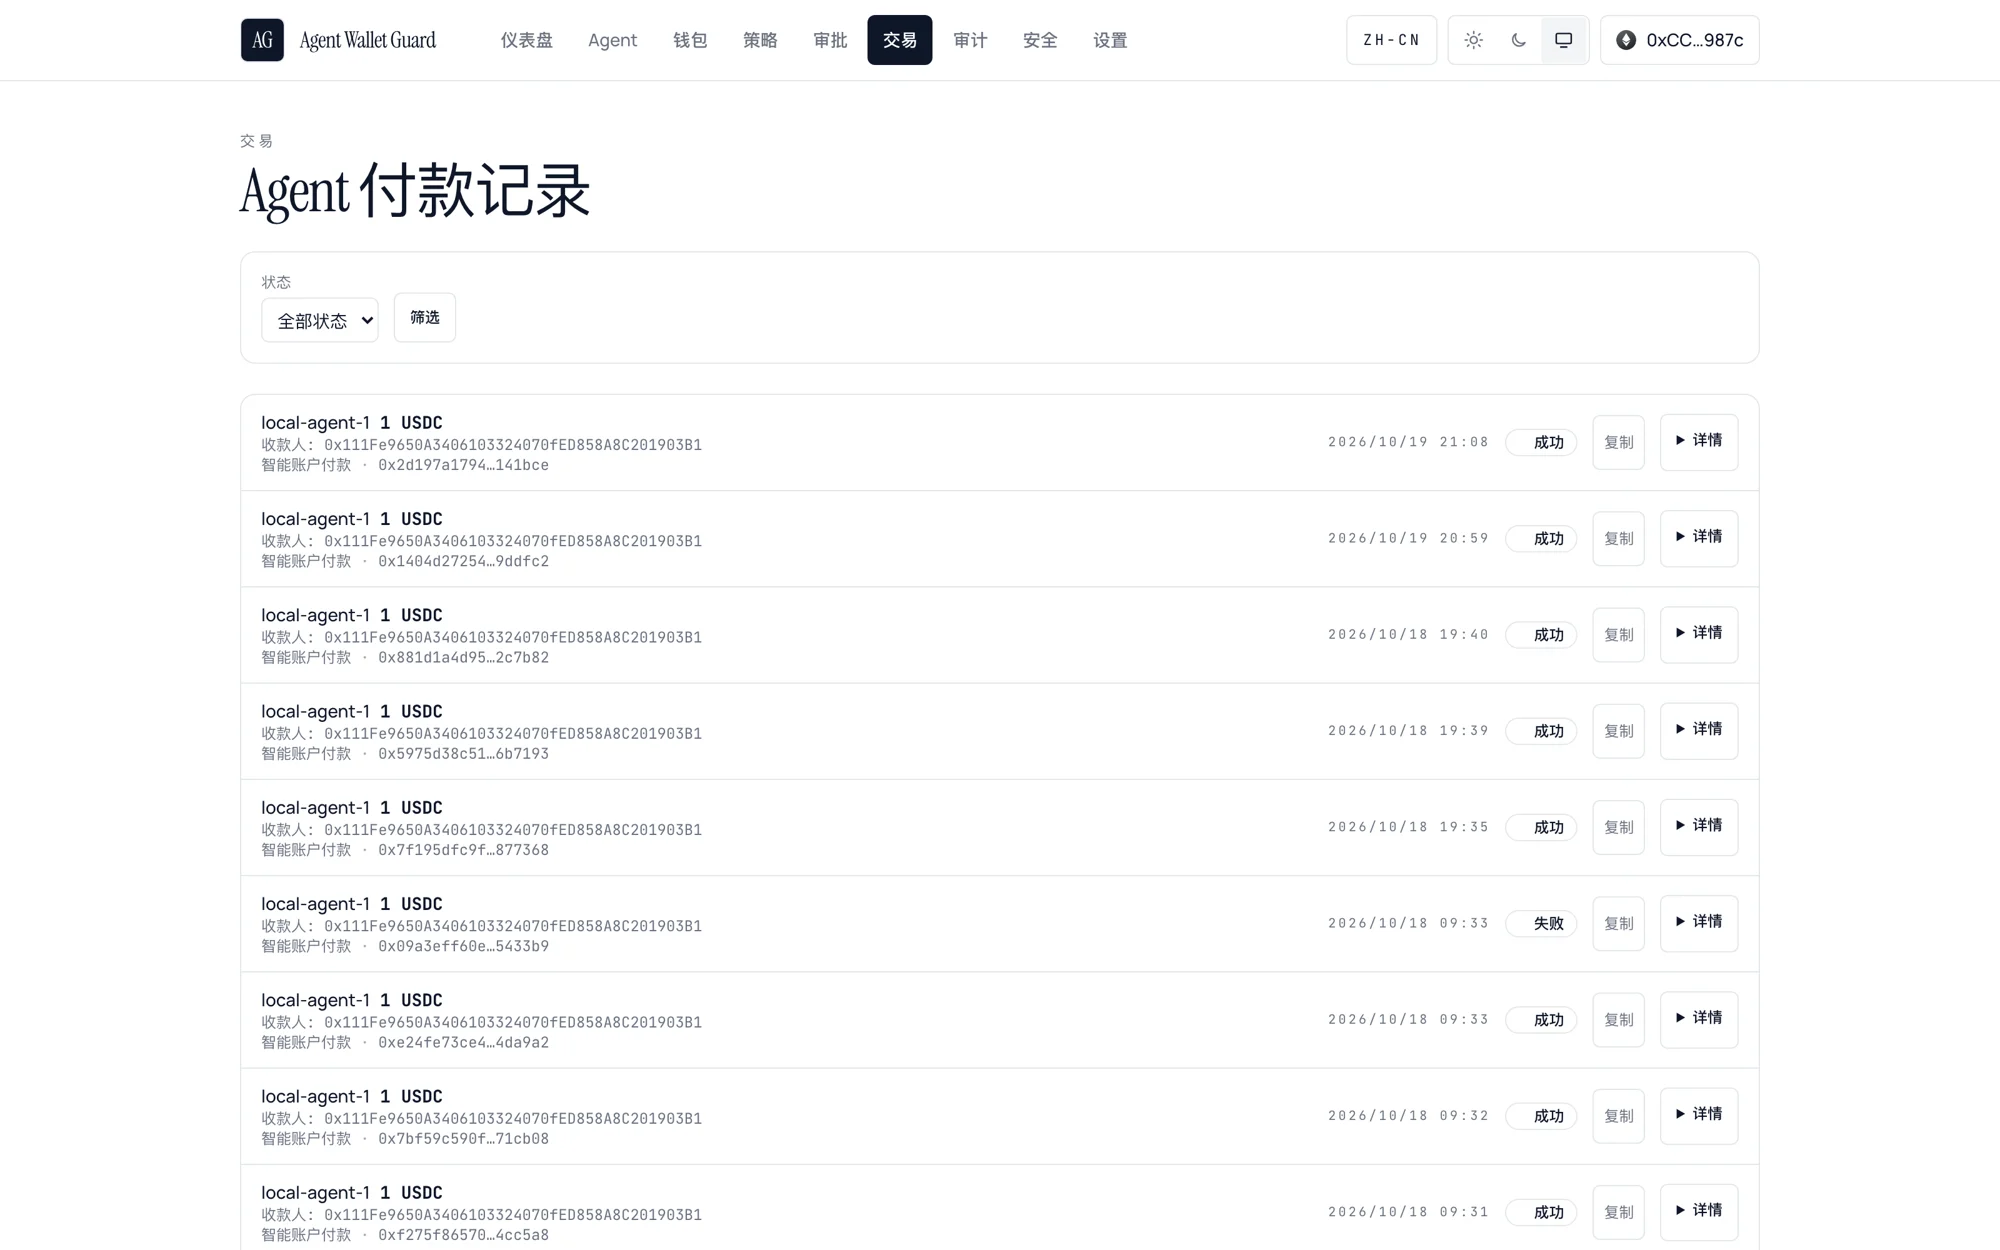
Payment historyDemo excerpt · Full screenshot
WHAT WE CAN BUILD WITH YOU
Your market. Your version.
These are customization directions. We agree what to retain, adapt and add before preparing an implementation proposal and quote.
01
A paid-data research assistant
Connect a provider, map queries to payment tasks and tailor limits, result delivery and cost reporting.
02
An enterprise automation platform
Add team or task budgets, approvals, organization sign-in, roles and cost centers for internal workflows.
03
An Agent permission center in a wallet
Integrate authorization lists, payment history, expiry reminders and revocation. Scope network and account compatibility separately.
BUILT BEHIND THE EXPERIENCE
See how the workflow is built.
01
Independent signing and smart accounts
A Node runner signs operations that pass through the API, Alto Bundler and EntryPoint into smart-account execution.
02
Guard verification
Guard validates authorization. The local demo also rejects an operation signed before revocation but submitted afterward.
03
State recovery
Separate chain confirmation from API registration. Retry synchronization without repeating a successful authorization transaction.
BUILT BY 0xF1 / 2026-10-19
What I’m building here
My development focus connects Owner authorization, an independent Node signer and smart-account execution, including revocation and recovery after synchronization failures.
Independent signing and smart accounts
Guard verification
State recovery
Can an old signature still execute after revocation?
The local demo submits a previously signed operation directly to the bundler after revocation; it is rejected on-chain. This differs from an API preparation limit check, so the page explains each verification layer separately.
What comes next
The permission-focused Owner workspace is implemented. Real providers, LLM decisions and full policy creation require separately scoped integration.